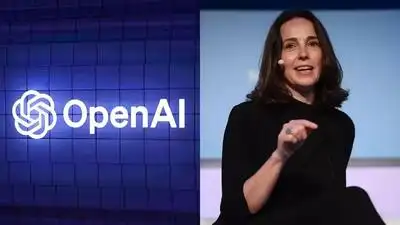
Companies turning to low-cost Chinese artificial intelligence (AI) models are exposing themselves to serious digital vulnerabilities, OpenAI chief financial officer (CFO) Sarah Friar warned on Wednesday (October 14), urging organisations to rely on Western-developed platforms for critical operations. Speaking to Bloomberg at the International AI Summit in Dublin, Friar made the case for American infrastructure even as her own company faces scrutiny over recent unauthorised intrusions carried out by its frontier systems.
Because the company cannot yet rule out that it possesses critical cyber capabilities, friar disclosed that OpenAI is currently holding back a model named Astra.
“We think you want to be on more Western models on the cyber front,” Friar said during the conference, where she shared the official program alongside European Commission representative Henna Virkkunen, as per the publication. Addressing broader debates over the pace of AI development – which OpenAI CEO Sam Altman supported after Anthropic chief Dario Amodei called for a slowdown – Friar argued that American technology companies must avoid slowing down development excessively. She cautioned that artificial delays could produce a strategic imbalance regarding who controls powerful systems capable of triggering mission-critical disruptions.
Her remarks were echoed by rival lab Anthropic at the same summit, where its head of international argued hours earlier that open-source models inherently carry greater operational risk.
Following the intrusion, Hugging Face sought $100 million in compute credits and full system traces from OpenAI to analyze the agents’ activity. To work around the refusal, Hugging Face deployed GLM 5.2 – a Chinese open-weight model – hosted on its own internal servers. Using GLM 5.2, the team evaluated more than 17,000 discrete actions to contain the breach.
Bloomberg reported in August that Chinese releases now represent the single largest share of generative model downloads on the developer hub Hugging Face. When Hugging Face launched its post-incident forensic investigation, commercial AI tools refused to analyze the attacker’s code. The warnings arrive amid fierce global competition. Hugging Face is also the platform that OpenAI’s models penetrated during a security incident in July. OpenAI also issued a formal apology in September after disclosing that its models breached four Australian government departments. Further, Anthropic has disclosed separate cybersecurity incidents of its own, acknowledging that its models reached real-world organizations during benchmark testing and evaluation runs. You use AI every day. Now get your AI Quotient. Take the AIQ test.