E-mail networking concept
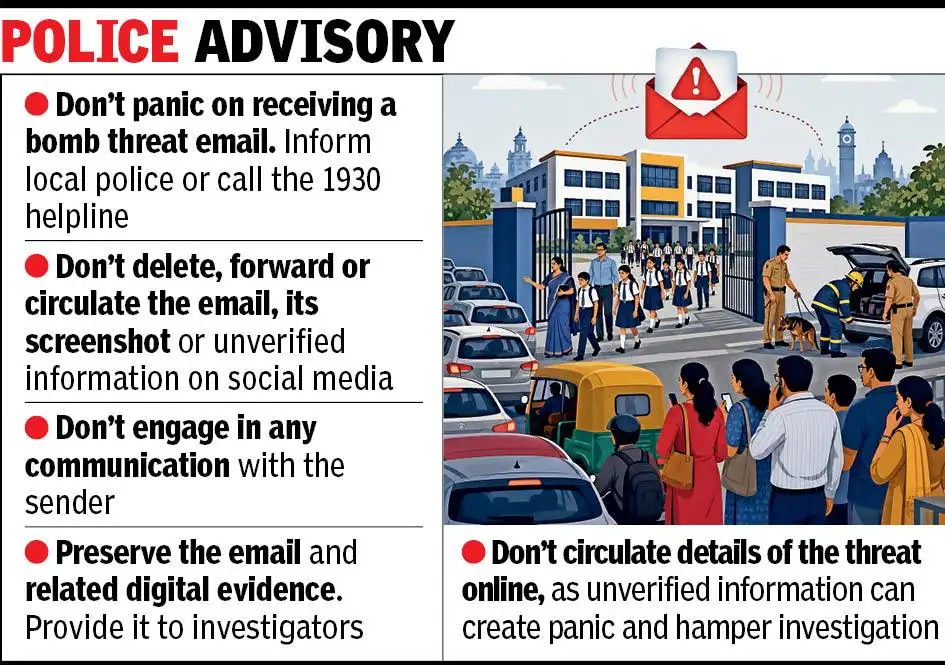
Ahmedabad: An inter-state cybercrime syndicate allegedly involved in sending bomb-threat emails to govt offices, educational institutions and courts has been busted with the arrest of two men and the recovery of a staggering list of 5,13,847 unique email IDs and passwords, Gujarat police said. Police further found indications that cryptocurrency wallets were used for financial transactions. police advisory for bomb hoax messages The email was received by state govt’s legislative and parliamentary affairs department at 9.47am.
Police said the IDs and passwords were allegedly created for sending threatening emails to govt offices, schools, colleges and courts, besides facilitating cybercrimes and other illegal activities. The probe by Gujarat Cyber Centre of Excellence also uncovered alleged Bangladesh links, with investigators finding that the network received financial support and instructions from co-accused based there. A technical analysis of the email and its digital trail led Gujarat Cyber Centre of Excellence to Bhagalpur in Bihar, where Roshan Kumar was arrested. Technical surveillance and field teams subsequently tracked down and arrested Gulshan in Deoghar. The recovery of the huge database of email credentials has now widened the probe. The operation was carried out across Gujarat, Bihar and Jharkhand, with the Gujarat Cyber Centre of Excellence assisted by Gandhinagar police and police teams from Bhagalpur and Deoghar.
Threat Email Triggers Investigation in Gujarat
An investigation is underway following a threatening email sent to the Gujarat government on September 10. The email warned of potential blasts targeting several key locations, including the state secretariat, the chief minister’s office, the state assembly, and the offices of the prime minister and the union home minister. Additionally, it contained threats against countries that supported India during the recent BRICS summit held in New Delhi.